Manage certificates securely. Reduce effort significantly.
With keyon true-Xtender, you gain a complete overview of your certificate landscape and automate the issuance, distribution, renewal and revocation of X.509 certificates. The modular suite helps companies establish secure, flexible and future-ready Public Key Infrastructure processes.
- Gain full transparency across your entire certificate landscape
- Automate certificate processes efficiently and securely
- Suitable for cloud, hybrid and on-premises environments




When certificates become a blind spot
Limited transparency, shorter certificate lifetimes and growing regulatory requirements are increasing the workload for PKI teams. Without a central overview and automated processes, expiring, unknown or incorrectly issued certificates can jeopardise the security and availability of business-critical systems.
62 %
of the IT managers surveyed do not know how many certificates they have
Without a complete and up-to-date certificate inventory, companies cannot reliably identify expiring, unused or incorrectly issued certificates. Centralised discovery and inventory are therefore essential for maintaining control over the certificate landscape.
47 days
maximum TLS certificate validity from March 2029
The maximum validity period for publicly trusted TLS certificates will gradually decrease to 47 days from 15 March 2029. Shorter validity periods significantly increase renewal frequency, making automated certificate processes increasingly important.
72 %
of the IT managers surveyed report that their teams are under increasing pressure
The growing use of cryptographic keys and certificates is placing additional pressure on PKI and IT teams. Automated certificate lifecycle management helps reduce repetitive manual tasks and makes expanding certificate landscapes easier to manage.
What keyon true-Xtender delivers for your PKI
The larger the certificate landscape, the more difficult it becomes to maintain a complete overview. true-Xtender brings essential PKI processes together on one platform, helping you maintain long-term control over operations, security and compliance.

Full transparency of your certificates
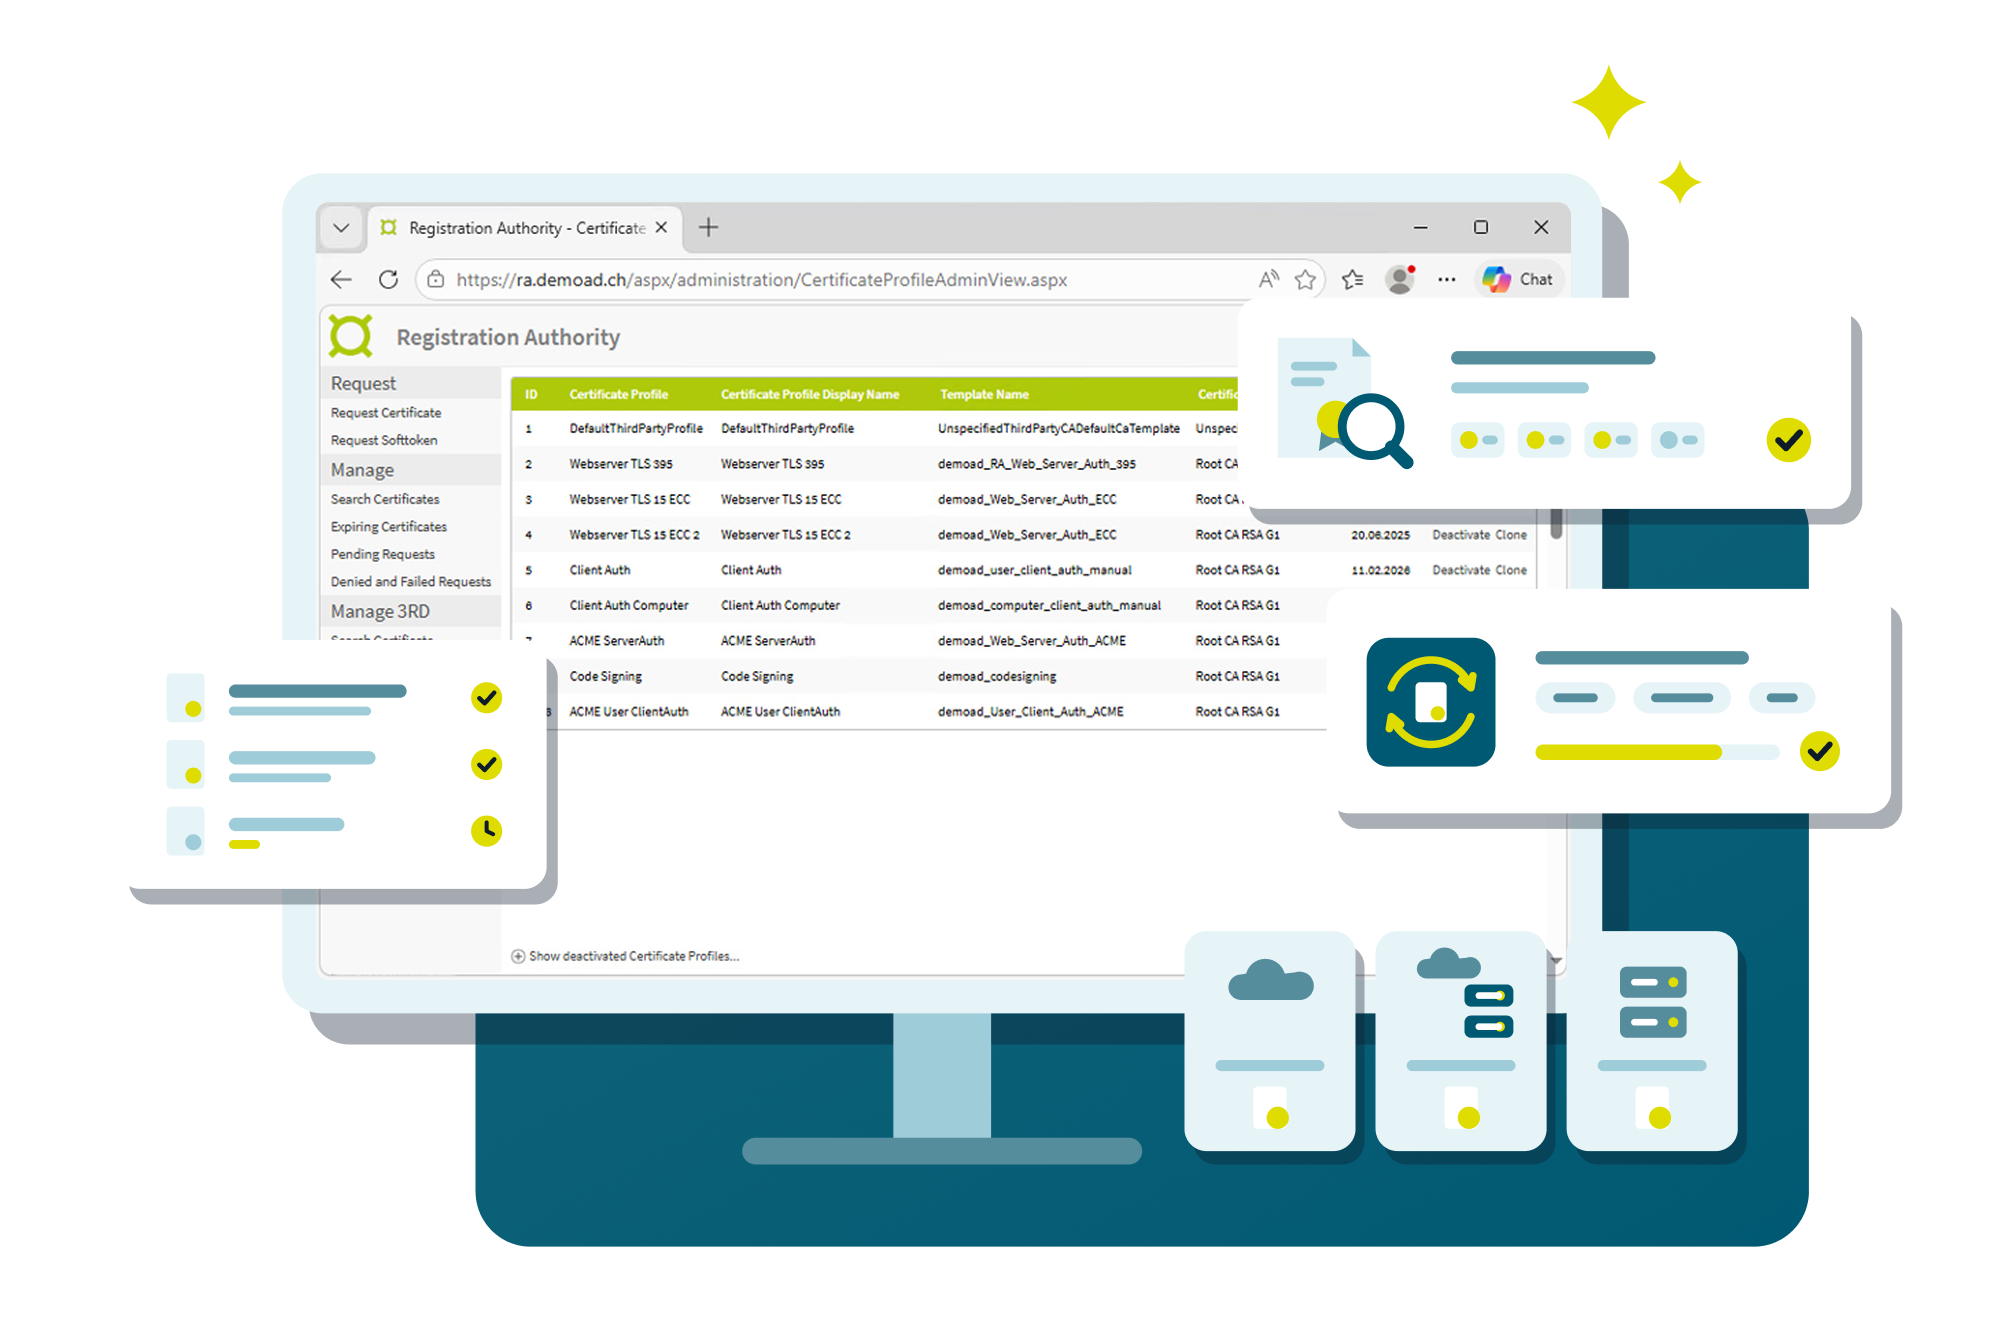
Discover and inventory certificates throughout your IT environment. true-Xtender Discovery consolidates discovered certificates in one central location, creating the foundation for reliable monitoring.

Automated processes instead of manual workflows
Automate certificate issuance and management using established protocols such as ACME, CMPv2 and EST. This makes even extensive and distributed PKI environments easier to manage efficiently.

Flexible integration into your infrastructure
Integrate certificate management into existing processes and system landscapes using web applications, REST and SOAP interfaces and various enrolment protocols.
How true-Xtender brings structure to your certificate management
From discovery and issuance to monitoring, true-Xtender brings together the key tasks of Certificate Lifecycle Management on a modular platform.
Detection
Identifying certificates and compiling a central inventory
true-Xtender Discovery searches your IT environment for existing certificates. Remote port scans and local agents for Windows, Linux and macOS systems can be used for this purpose. Discovered certificates are transferred to the true-Xtender Registration Authority, where they become available for monitoring and further processes. This provides PKI teams with a consolidated overview of certificates in files, local certificate stores, applications and network services.

Automation
Automatically issue and distribute certificates
The true-Xtender Registration Authority connects your certificate authorities with applications, devices and users. Established protocols such as ACME, CMPv2 and EST, together with REST and SOAP interfaces, enable certificates to be issued, renewed and revoked automatically.
The proxy architecture supports deployment across separated network zones. Certificate processes can therefore be automated without giving every client system direct access to the certificate authority.

Monitoring
Ablaufende Zertifikate frühzeitig erkennen
The true-Xtender Third-Party Certificate Manager monitors certificates from third-party providers. Certificates can be imported through the web interface or a web service interface and supplemented with additional metadata.
Multiple notification services alert the responsible users before a certificate reaches the end of its validity period. This allows renewals to be initiated in time and helps prevent avoidable service interruptions.

Guidelines
Consistently enforce certificate policies
The true-Xtender Policy Module extends Microsoft ADCS with rule-based issuance and management of X.509 certificates. Certificate content and extensions can be checked, supplemented or adjusted according to predefined requirements.

Common challenges in certificate management
The requirements placed on modern PKI environments continue to grow. true-Xtender helps companies address common challenges involving transparency, automation and compliance.
Limited visibility across certificates
Many companies do not know exactly where certificates are used, who owns them or when they expire. This creates security risks and unnecessary operational effort. true-Xtender Discovery identifies, inventories and monitors certificates across the entire IT landscape. This establishes a reliable foundation for operations, compliance and further automation.

Automatically issue and renew certificates
Shorter certificate lifetimes are placing increasing pressure on PKI teams. Manual renewal processes are prone to errors and difficult to scale. Using ACME, CMPv2 and EST, true-Xtender automates the issuance, distribution and renewal of certificates, significantly reducing manual effort.

Identify certificate expiry risks in time
Expired certificates remain a frequent cause of preventable service interruptions. The Third-Party Certificate Manager centrally monitors certificates and alerts responsible teams before certificates reach critical expiry dates.

Consistently enforce certificate policies
In regulated industries in particular, policies and approval processes must be implemented in a traceable manner. The Policy Module adds rule-based checks to existing PKI environments and helps ensure that certificates are issued in a controlled and consistent way.

Efficiently operate your own certificate authorities
Operating multiple Root and Issuing CAs can require considerable administrative effort. With keyon true-CA, certificate authorities can be managed centrally, new hierarchies can be deployed more quickly and different enrolment protocols can be integrated.

The right solution for your certificate landscape
keyon true-Xtender is available as a perpetual licence with annual maintenance and support or as a subscription. Essential and Pro are available for standardised requirements, while the Enterprise model allows for an individually configured solution.
Essential
Price on request
For companies looking to establish a central foundation for certificate management.
- true-Xtender RA Web Application
- true-Xtender RA Web Service Add-on
- Third-Party Certificate Manager
- Up to 250 certificates per year
- Two CA connections
- Can be extended with one add-on for ACME, EST or CMP
- One proxy instance
Pro
Price on request
For larger certificate landscapes requiring additional CA connections and higher certificate volumes.
- true-Xtender RA Web Application
- true-Xtender RA Web Service Add-on
- Third-Party Certificate Manager
- Up to 500 certificates per year
- Four CA connections
- Can be extended with one add-on for ACME, EST or CMP
- One proxy instance
Enterprise
Price on request
For complex PKI environments that require a flexible combination of modules and add-ons.
- All modules and add-ons available
- Unlimited number of certificates
- Modular and configurable functionality
- Individual pricing
Integrated into your PKI infrastructure
true-Xtender connects certificate authorities, enrolment processes and validation services within a central architecture. Standardised protocols and interfaces allow automated and manual certificate processes to be integrated into existing infrastructures. The architecture supports private and public CAs as well as modern client, server and IoT environments.
Companies have different requirements regarding operations, security and compliance. true-Xtender can therefore be operated in fully independent environments or provided as a managed solution. This allows the platform to be adapted flexibly to existing infrastructure and operating models.
Available options:
- On-premises
- Private cloud
- Hybrid
- Managed service
true-Xtender supports a wide range of established enrolment protocols, interfaces and integration standards, allowing existing systems and processes to remain in use. Certificates can be issued, managed and deployed automatically across different environments.
Supported standards:
- ACME
- CMPv2
- EST
- REST API
- SOAP
- Microsoft DCOM
- CEP/CES
Would you like a concise overview of the most important functions, modules and potential applications? The product data sheet provides a compact summary of the architecture, licence models and primary use cases of keyon true-Xtender.
From installation to configuration, the technical documentation provides administrators and PKI managers with detailed information about modules, interfaces, supported protocols and technical requirements.


Frequently asked questions about keyon true-Xtender
true-Xtender is available both as a traditional perpetual licence and under a subscription model. With the perpetual option, you purchase the software for permanent use and additionally obtain annual maintenance and support.
The subscription model offers predictable ongoing usage with regular updates and support services. The most suitable option depends on your organisational requirements, planned usage and financial model. Our experts can advise you on selecting the appropriate option.
Essential and Pro are available for standardised deployment scenarios. Essential provides a central foundation for certificate management, while Pro is designed for larger certificate landscapes with additional CA connections and higher certificate volumes. For more complex requirements, the Enterprise model provides a modular approach. Individual components and add-ons can be combined according to the relevant PKI environment and requirements. Prices for all packages are available on request.
Companies have different requirements regarding data protection, operations and infrastructure. true-Xtender can therefore be operated on-premises, in a private cloud, as a hybrid solution or as a managed service. This flexibility allows the platform to be aligned with existing security and compliance requirements as well as individual infrastructure and operating models.
Yes. Our PKI experts support companies with the planning, implementation and operation of true-Xtender. This includes architecture consulting, technical implementation, the migration of existing environments and support during ongoing operations. Customers therefore benefit not only from the software itself, but also from extensive experience in Public Key Infrastructure and Certificate Lifecycle Management.
true-Xtender can be purchased directly from SITS or through your preferred software supplier. To receive a quote tailored to your requirements, use the contact form on the product page.
Yes. SITS Sales Engineers and Consultants can demonstrate the application live and answer questions about possible deployment scenarios, modules and integration into your existing PKI environment. You can request the demo using the contact form on the product page.
Learn more about certificate management
Public Key Infrastructure and certificate management
Learn how Enterprise PKI and X.509 certificates can be used for secure authentication, encrypted communication and automated certificate management.
Digital signatures for secure processes
From contracts and official notices to business-critical documents, digital signatures provide integrity, authenticity and legally compliant business processes.
Bring transparency to your certificate landscape
Experience in a personal demo how keyon true-Xtender centrally discovers certificates, enables automated processes and integrates into your existing PKI infrastructure.
You are currently viewing a placeholder content from HubSpot. To access the actual content, click the button below. Please note that doing so will share data with third-party providers.
More Information